Information security risk assessment
Prepare or review information security risk assessment, agree the responsible owner and organize evidence that shows the process is being used.
Information risks, security control ownership and evidence for an ISMS.
Operating context
Rektrs supports information security management through a scoped assessment of your operations, existing records and process responsibilities. The engagement translates the agreed standard into practical documentation, working routines and review evidence.
The applicable edition, exclusions where permitted, locations, sector obligations and assessment route are confirmed at scoping. The roadmap is based on actual gaps and evidence; documentation alone does not demonstrate effective implementation.
An evidence-based preparation plan with responsibilities and assessment dependencies made clear.
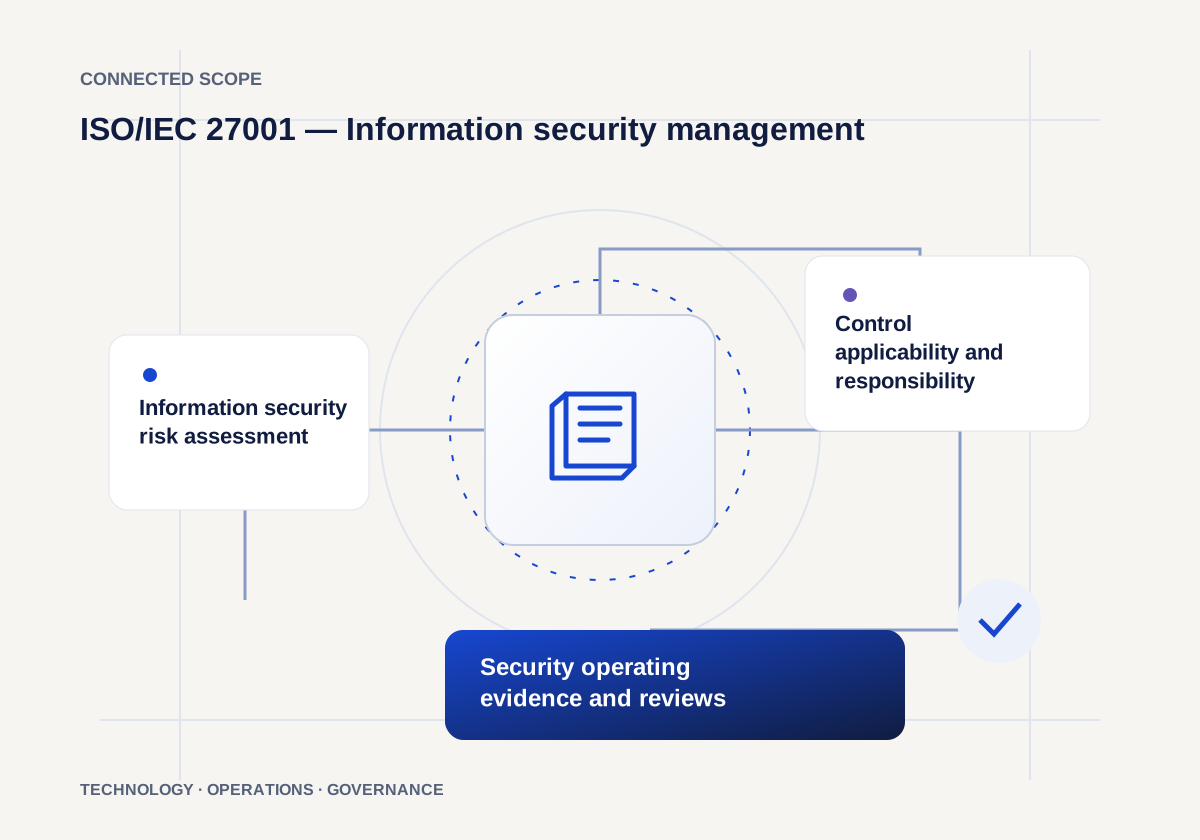
Prepare or review information security risk assessment, agree the responsible owner and organize evidence that shows the process is being used.
Prepare or review control applicability and responsibility records, agree the responsible owner and organize evidence that shows the process is being used.
Prepare or review security operating evidence and reviews, agree the responsible owner and organize evidence that shows the process is being used.
Plan your engagement
Rektrs supports ISO 27001 readiness through gap assessment, documented responsibilities, implementation and internal review. The scope addresses risk assessment, control selection, access management and security evidence.
Rektrs provides consultancy and readiness support. A separate competent assessment body evaluates conformity and decides the outcome. ISO 17025 concerns laboratory accreditation; ISO 31000 is guidance, not a certifiable management-system standard.
Before implementation
We confirm your current systems, locations, process owners and required outputs. The proposal sets milestones, dependencies, acceptance criteria and support responsibilities for the agreed scope.
Certification, if sought, is assessed and decided by an independent certification body. REKTRS provides consultancy and preparation; ISO itself does not certify organizations.
Official ISO standard overview