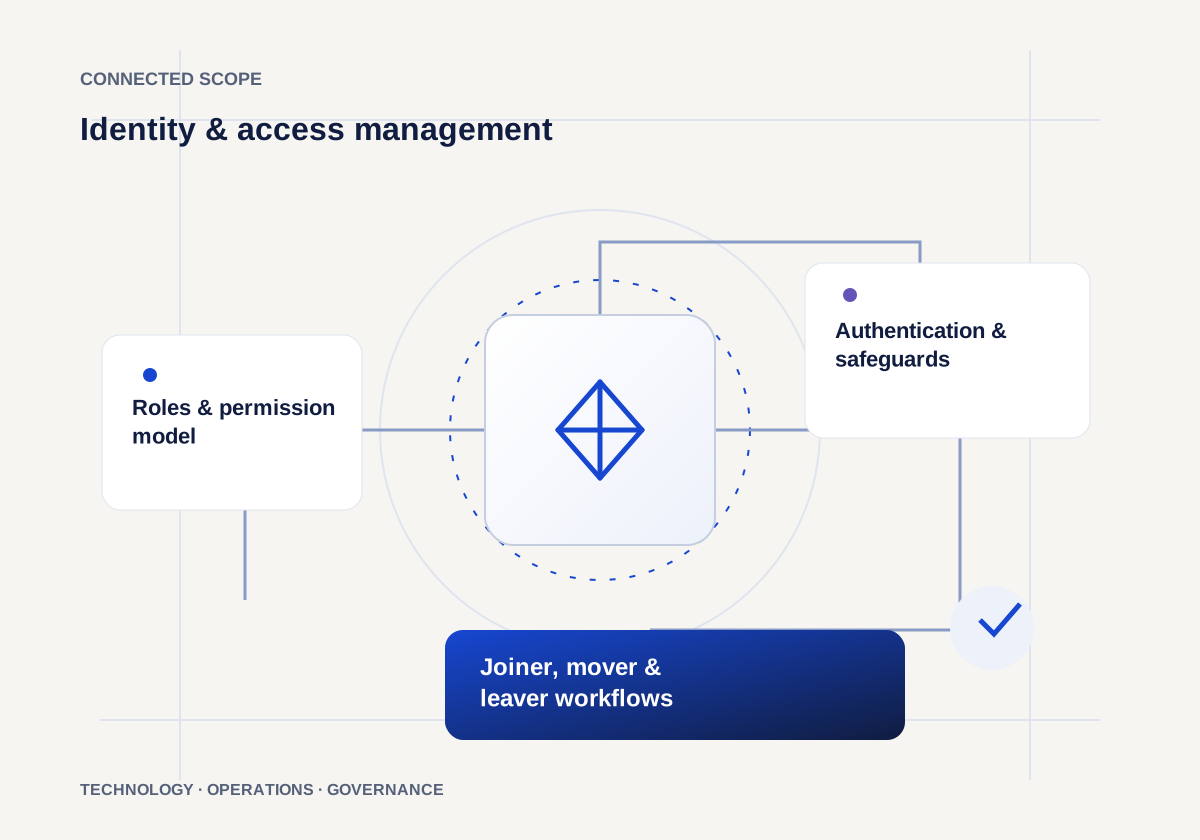
Roles & permission model
Map responsibilities to appropriate application and data access.
Make access permissions understandable, approved and reviewable.
Operating context
Secure access begins with named roles, accountable approvals and an owned process for joining, changing role and leaving.
An owned implementation, agreed review criteria and a maintainable handover.
Map responsibilities to appropriate application and data access.
Support agreed multi-factor and account-control settings.
Connect approvals, provisioning and removal to owned business events.
Prepare review evidence and track exceptions or overdue actions.
Before implementation
We confirm your current systems, locations, process owners and required outputs. The proposal sets milestones, dependencies, acceptance criteria and support responsibilities for the agreed scope.